
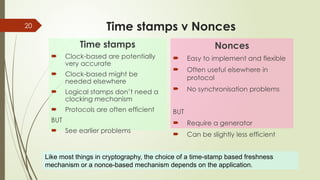
Nonces can be used in network protocols to ensure message freshness and prevent replay assaults. In security engineering, nonce is an abbreviation of quantity used once1 (it is analogous in spirit to a nonce word). It is commonly a random or pseudo-random number issued in an authentication protocol to guarantee that old communications can’t be reused in replay assaults. For instance, nonces are utilized in HTTP digest entry authentication to calculate an MD5 digest of the password.
How Is A Nonce Used In Encryption?
It might help you to avoid utilizing the CSP unsafe-inline directive, which might allowlist all inline scripts or types. Nonces may be generated and utilized in various methods, depending on the requirements of the cryptographic system or protocol. A digital foreign money that is secured by cryptography to work as a medium of trade within a peer-to-peer (P…
How Is Nonce Used In Blockchains?
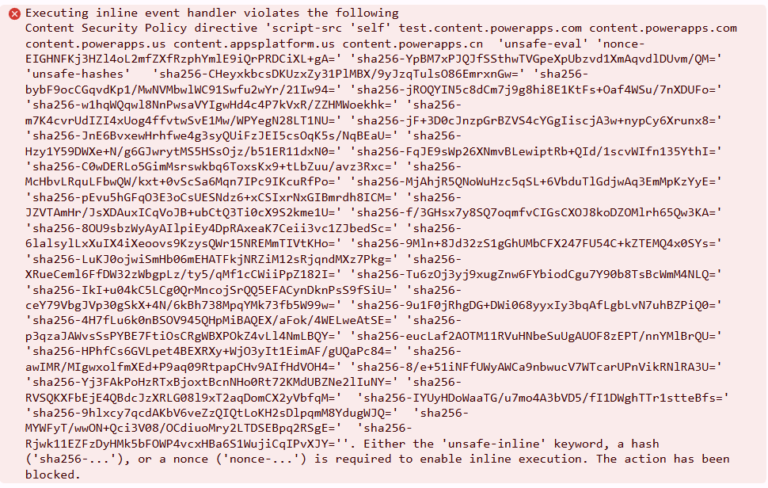
Nonce is the arbitrary number that miners must give you — essentially guess — to supply a number lower than or equal to the goal hash. E-commerce provider PayPal makes use of nonces in its encryption scheme to send sensitive fee information. This helps the corporate adjust to the Cost Card Business Knowledge Safety Normal. Bizarre that lots of people from right here don’t understand your utilization of the term. SSP is a groundbreaking, open-source, self-custody, BIP48 multi-signature browser pockets for a number of blockchains with Account Abstraction. The nonce attribute is helpful to allowlist specific parts, corresponding to a particular inline script or fashion elements.
Hardware wallets deal with ECDSA nonce era within their secure elements, utilizing devoted hardware random number generators that present high-quality entropy. These implementations are typically licensed to satisfy cryptographic standards like FIPS 140-2, offering assurance of correct nonce randomness. Users can not and mustn’t try and specify nonces manually when using hardware wallets—the system handles this routinely. Yes, a nonce is often included in the knowledge https://www.m-sedan.com/ipod_usb_mp3_control_y_if_equipped-2487.html being hashed, particularly in blockchain mining.
Second, in transaction administration, they enforce uniqueness, guaranteeing that each switch is processed exactly as soon as and in sequence. The two uses share a cryptographic origin however serve distinct capabilities relying on the chain and context. Nonetheless, it might be less likely to be distinctive as a result of there is a probability that the identical random number could be generated more than once. Usually, a nonce is a worth that varies with time to confirm that particular values aren’t reused. A nonce could be a timestamp, a visit counter on a webpage or a particular marker meant to limit or prevent the unauthorized replay or copy of a file. For hash features, the initialization vector is a constant that never changes.
On The Word “nonce” In Cryptography And The Uk
- Proper nonce era for ECDSA requires a cryptographically safe random quantity generator (CSRNG) that produces uniformly distributed values across the complete vary 1, n-1 where n is the order of the elliptic curve.
- Every time a new session is started, or a transaction is made, a unique nonce should be generated to make sure the best level of security.
- Send inquiries about terminology to the Supply’s authors; NIST publications will often embrace a contact e mail for that Source.
- Nonce (Number Used ONCE) is a random or sequential value that is used solely as soon as in a cryptographic communication to forestall replay assaults.
- Systems guarantee the distinctiveness of a nonce by way of various strategies, relying on the application and its necessities.
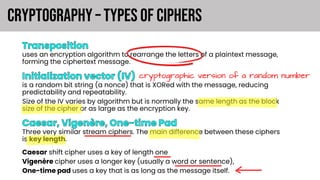
For brevity, iv is tantalizingly convenient (but so is n), so that you typically see IV shoehorned in all places.
Does Nonce Measurement Matter In Cryptographic Applications?
In cryptographic protocols like TLS, nonces assist make positive that every session is unique. Nonces forestall replay assaults the place an attacker captures a legitimate authentication request (e.g., OAuth authorization code, SAML assertion) and resends it to achieve unauthorized access. Without nonces, an attacker could seize a login request and replay it to authenticate as the victim. Nonces guarantee every authentication transaction is exclusive and may only be used once. LoginRadius employs nonces throughout our authentication platform for replay assault prevention. Our OAuth 2.0/OpenID Join implementations use nonce parameters, authorization codes are single-use nonces, and password reset/email verification tokens are time-limited nonces.
